Cybersecurity Training for Employees in the Form of a Series
In this article
- Cybersecurity training – why is simply getting through it not enough?
- Organisational cybersecurity training – what is the goal and the programme?
- Phishing, ransomware, client work and remote work – where do threats show up today?
- What is the Gamfi cybersecurity training series?
- Cybersecurity training for employees, performed by actors – how does it work?
- Why take part in training on network security and personal data in the form of a series?
- How long does the training take, what do I need beforehand, and what can I expect?
- FAQ – common questions about cybersecurity training
Cybersecurity is another way of saying: the rules of using the internet safely. A course on systems security is a serious matter. And yes, you can put together a slide deck, send out a PDF, add a test and tick the topic off. Except that security, online and of the network itself, is not decided on slide 37. It is decided in everyday work. In whether someone clicks a suspicious link, sends unencrypted files, can tell phishing from an ordinary message from a client, and whether basic cyber hygiene survives working from home, from a phone and on the road…
Managing risk in this area rests on knowing the rules of data protection well. That is why, for subjects such as company data security, a training series works surprisingly well. It shows real business situations, puts knowledge in the context of company life, and builds awareness of threats where it actually matters.
Cybersecurity training – why is simply getting through it not enough?
In many companies, security online is still "a topic for IT". The problem is that most incidents start much earlier, for example when someone in a hurry clicks an ordinary link.
Every area of employee security matters: everyday caution, safe working practices, knowing the procedures and being able to react. Especially when a security breach does happen.
An employee does not need to be an expert in IT architecture to strengthen the organisation's level of cybersecurity. They do, however, need answers to these questions:
- What does a good password look like, and what does password security involve?
- What is phishing, and what is the risk?
- How do I protect personal data and data security?
- How do I handle data processing safely?
- What does safe remote work look like?
- What does mobile device security involve?
- What are the ways to protect data in everyday work?
Without that knowledge, even the best technical safeguards will not do the job. Information systems security and IT/OT infrastructure cybersecurity only start working in tandem with an aware human being.
Organisational cybersecurity training – what is the goal and the programme?
The goal is simple: employees should know how to work safely. Training in the basics of cybersecurity should therefore cover subjects such as:
- basic security rules and safe working practices,
- data protection rules,
- information protection and its scope,
- company data security (backups as one of its building blocks),
- service security, cloud service security and network security,
- data storage and data processing,
- physical data security,
- mobile device security,
- cybersecurity of remote work,
- managing data security, managing risk and business continuity.
This is not about an academic list of terms, but about preparing people for their actual work.
Training employees in data security – what do they need to know?
A well-built programme answers these questions:
- What are the most common cyber threats today?
- What do phishing, spoofing and online scams look like?
- What do I do if data leaks?
- How do I recognise examples of attacks?
- How do I protect files I send?
- Can I use public hotspots safely?
- What does working on a mobile device outside the office look like?
- How do I make remote communication work without unnecessary risk?
Does that sound complicated? It is, because the scope here really is broad. Which is exactly why training has to fit the organisation. A retail team learns from different situations than logistics, head office staff or people working remotely.
Phishing, ransomware, client work and remote work – where do threats show up today?
The biggest problem with conventional courses is that they leave out context. And practical examples of threats are precisely what employees need most.
Picture a few situations.
An employee receives an email from a "supplier" asking them to log in urgently. That may be phishing.
Someone opens an attachment with a supposed invoice. Ransomware may be running in the background.
A specialist works from a café, connects through a public network and is not sure whether to use the hotspot. That is the cybersecurity of remote work.
A consultant sends a client a report but gets the email address wrong. That is how security breaches and problems with processing personal data begin.
On top of that come questions of:
- working in public places,
- remote work,
- working with clients,
- working on a mobile device,
- files being sent,
- mistakes in storing data,
- careless handling of what personal data actually is.
As you can see, these are not extreme cases but everyday ones. And if that is so, training has to show exactly these situations. Otherwise an employee knows the rules but cannot apply them.
What is the Gamfi cybersecurity training series?
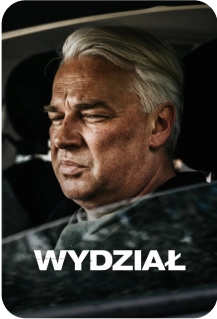
Five episodes, 33 minutes of story. The series „Wydział" follows an investigative team through one type of cyberattack after another. Polish audio with English subtitles.
A frame from „Wydział". Employees get a case to solve rather than a list of rules to read – and they learn from the decisions the characters make.
A Gamfi training series is a story-driven course built on microlearning, where each episode covers a different area of security. The obvious ones, such as phishing and ransomware, but also those that keep appearing in everyday work: attacks on social media, threats tied to phones, AI-based manipulation, deepfakes and spear phishing.
That matters, because cybersecurity is not limited to the work computer. It also covers the private phone used for logging in, messaging apps, social media, online shopping, fake invoices and situations where a fraudster poses as someone credible.
A training series:
- shows practical examples of threats and builds awareness of them,
- teaches how to react to security incidents,
- puts the areas of employee security in order, step by step,
- supports cyber hygiene and digital resilience across the organisation.
The series does not stop at "be careful" – it shows what exactly to watch out for and what to do when a threat really does appear.
Cybersecurity training for employees, performed by actors – how does it work?
Cybersecurity training in the form of a series works well not because it is more interesting than a slide deck, but because it is closer to how people actually learn. The material is split into short episodes rather than one long lecture. Each one shows a specific business situation, a decision and its consequences. That way employees learn to recognise the moments that call for particular care.
A training schedule can look like this:
- Episode 1: An introduction to cybersecurity. Social engineering, spoofing, smishing. A good starting point for building awareness and grounding the subject in everyday work.
- Episode 2: Ransomware and double extortion – prevention and a response plan. This stage develops the subject of ransomware, how an organisation responds, and how to connect prevention with business continuity.
- Episode 3: Phishing, deepfakes, vishing, smishing – how do you spot them? A module that matters particularly now, when AI-assisted scams are increasingly convincing.
- Episode 4: Attacks on social media, payment-app fraud, strong passwords, 2FA, account recovery. Here the emphasis falls on password security, two-factor authentication, attacks on social media and practical rules for protecting accounts.
- Episode 5: Deepfakes in more depth. Invoice-swap scams, the economics of fraud, how to shop safely. This module shows that cyber threats do not end with the work inbox. They also cover purchases, payments, impersonating business partners, and scenarios that cross between work and private life.
Why take part in training on network security and personal data in the form of a series?
Search for terms like cybersecurity training for employees, basics of cybersecurity training or data protection rules, and you will quickly see the market is full of offers. So why do organisations choose e-learning and training series?
Because this format:
- is engaging, which makes the course easier to get through and to remember,
- shows practical examples of threats,
- puts the areas of employee security in order,
- strengthens company data security,
- helps ground personal data protection in everyday work.
It is also easy to run. There is no need to take whole teams out for several hours, employees can work through the material in stages, and the organisation can see progress, results and completion.
How long does the training take, what do I need beforehand, and what can I expect?
The length depends on scale and depth, but well-designed cybersecurity training for employees should not overload anyone.
A training series arrives in short episodes, one subject at a time. Each subject closes with a test that reinforces what was learned, and automatic reminders go out to anyone who falls behind.
Can you expect training suited to how people work today? You can – what it delivers is:
- knowledge grounded in real, everyday situations,
- material fitted to the organisation,
- sharper attention to cyber threats,
- a better grasp of what security breaches and incidents actually are,
- stronger habits: password security, cyber hygiene and safe use of tools.
Information security training as a series – can I choose between a closed and an open course?
There are several options. Companies can choose a closed course, an industry-specific programme, or a set of materials assigned as part of onboarding. One thing matters most: the training has to be useful and grounded in the work itself.
If you are wondering about prerequisites, they are usually not technical. This is not a course for administrators, but training for people who work every day with information, clients, systems, devices and documents.
Does your team need material like this? Let's talk about Gamfi.
FAQ – common questions about cybersecurity training
Is cybersecurity training only for the IT department?
No. Cyber hygiene is needed across the organisation, because every employee affects information protection and company data security.
What subjects should the programme cover?
A good programme covers password security, personal data protection, data processing, safe remote work, mobile device security, cloud service security and responding to security incidents.
Can the training be fitted to our organisation?
Yes. Effective training should be fitted to the organisation, its industry, processes, risks and working environment. Without that, building real awareness of threats is hard.
Which matters more: the certificate or the change in behaviour?
From the company's point of view, the change in behaviour. Completing a course does not raise the organisation's level of cybersecurity if employees still ignore the basic rules.
Does e-learning really work in such a practical area?
Yes, as long as it is not simply a lecture moved online. Well-designed e-learning with a story and scenarios shows practical examples of threats better than a conventional presentation.
What risks should every employee understand?
Everyone should recognise cyber threats, know examples of attacks, understand what a data leak can cost, how to protect files they send and how to respond to a security breach.
Can the training also cover remote work and working in public places?
The cybersecurity of remote work is now a compulsory part of any programme, as are working in public places, remote communication and working on a mobile device.
Which technical areas are worth covering?
It is worth explaining, in plain terms, subjects such as network security, service security, cloud service security, information systems security, IT/OT infrastructure cybersecurity and operating system security. Not to turn employees into administrators, but so they understand where the risk begins.